
PDPA: The Why and How of Implementation
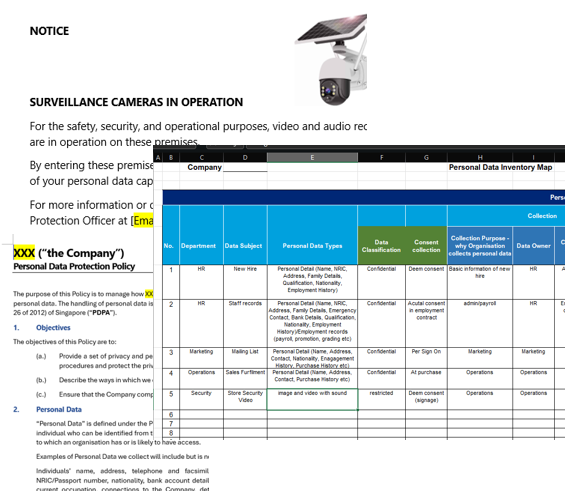
If you run a business in Singapore, handling personal data is no longer optional—it is regulated by the Personal Data Protection Act (PDPA). Introduced in 2012, this law sets clear rules for collecting, using, disclosing, and retaining personal data, covering everything from names and contact details to NRIC numbers, bank information, and family particulars. For many business owners, compliance feels like another administrative burden, but it is far more than that. It is your legal shield, your brand asset, and a way to build lasting trust with customers. Non‑compliance carries heavy consequences: fines up to SGD 1 million or 10 % of your annual turnover, whichever is higher, plus reputational damage that can take years to repair. When you implement PDPA properly, you reduce risk, improve operational efficiency, and stand out as a responsible organization in a competitive market.
Successful implementation follows nine core obligations outlined in the PDPA, and the policy framework used by Headington Management shows exactly how to put these rules into practice. First, consent and purpose limitation: you must collect data only for clearly stated, reasonable purposes, and not require excessive data as a condition of service. Individuals can withdraw consent anytime, and you have 30 days to process such requests. Second, access, correction, and accuracy: customers have the right to view their data and fix errors; you must keep records accurate, especially if used for decisions or shared with third parties. Third, protection, retention, and transfer: use both physical safeguards—locked cabinets, document shredding, need‑to‑know access—and technical controls like encryption, secure networks, and regular software updates. Keep data only as long as needed, and if transferring outside Singapore, ensure protection matches PDPA standards. Appointing a Data Protection Officer (DPO) is also required to handle inquiries, complaints, and internal reviews, with a clear process to respond within 14 working days.
Putting all this together can be overwhelming, especially for small and medium enterprises with limited legal or IT resources. That is where Headington Management makes the difference. We provide a complete, tailored PDPA framework—from drafting compliant policies like the one referenced here, to training staff, setting up security measures, and managing complaints or consent requests. Our DPO services ensure you always have an expert point of contact, and we update your practices as laws evolve. With Headington Management, you do not just “check a box”; you build a sustainable data‑protection culture that protects your business, reassures your clients, and turns compliance into a long‑term advantage.


Comments